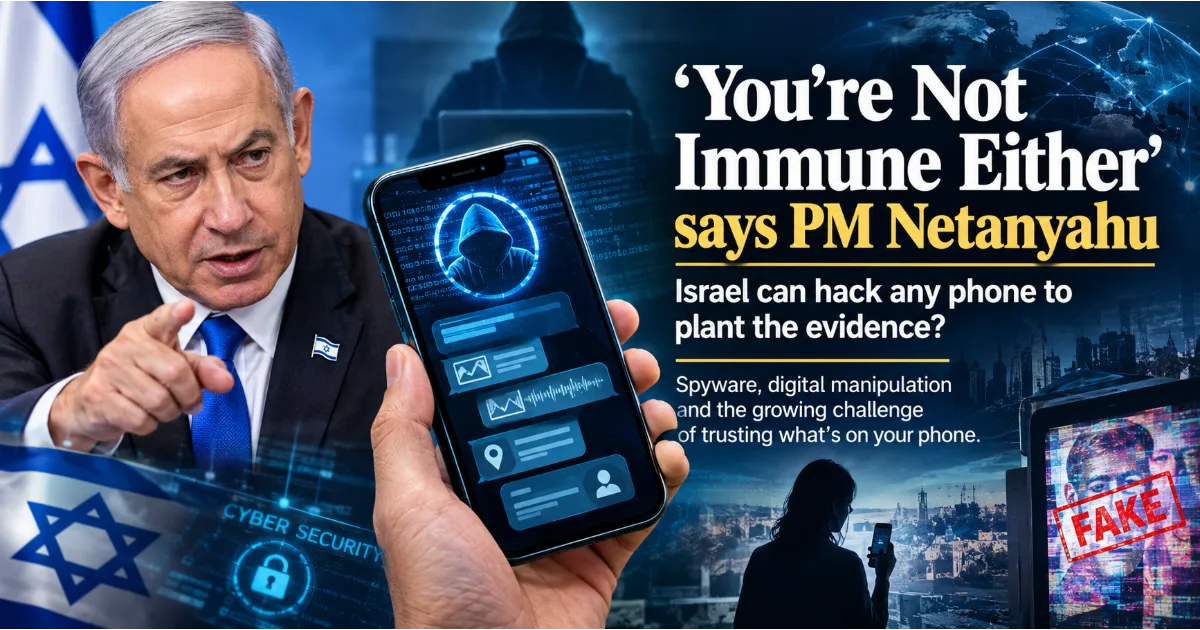
Israeli Prime Minister Benjamin Netanyahu's warning to CBS journalist Major Garrett about the vulnerability of smartphones has drawn renewed attention to a question that is becoming increasingly important in the digital age: how much can a person really trust the information stored on a phone? During an interview broadcast by CBS in May 2026, Netanyahu picked up Garrett's smartphone and warned that the device could be penetrated and used to construct damaging claims about its owner. “You're not immune either,” Netanyahu told Garrett, explaining that someone could penetrate the device and say almost anything about him. Netanyahu then argued that if such claims were repeated often enough, people could eventually believe them.
The remarks were made in the context of Netanyahu's broader argument about social media and Israel's struggle over its international image during the war. He described social media as another front in the conflict and connected the spread of damaging narratives to the enormous influence of digital platforms. His comments were not, by themselves, a statement that Israel routinely hacks journalists' phones or that the Israeli government can fabricate evidence on any device. That distinction is important. At the same time, the underlying technological concern he raised is real. Sophisticated commercial spyware exists, some of it can penetrate smartphones without the user's knowledge, and researchers have documented cases in which highly intrusive surveillance tools developed by Israeli companies were used against journalists, politicians, activists and other individuals around the world.
The phrase “Israel can hack any phone to plant the evidence” therefore needs to be examined carefully. There is substantial evidence that sophisticated Israeli-developed spyware can compromise certain smartphones under particular circumstances. There is not reliable evidence establishing that Israel possesses a universal capability to hack every phone or that every piece of digital evidence on a compromised device can automatically be dismissed as fabricated. The difference between those two propositions is enormous. It is also the difference between a serious cybersecurity discussion and a claim that goes beyond the evidence.
What makes Netanyahu's comments particularly striking is that they touch on a problem extending far beyond Israel. Smartphones have become personal archives containing years of conversations, photographs, documents, location information, contacts and financial information. They are simultaneously communication devices, cameras, microphones, authentication tools and repositories of personal history. If a sufficiently sophisticated attacker gains access to such a device, the consequences can be far more serious than simply reading someone's messages. The possibility of surveillance raises a second question that is becoming increasingly important: can information on a compromised device still be treated as an unquestionable record of what its owner did?
That question has become more relevant as spyware technology has advanced. Pegasus, developed by the Israeli company NSO Group, is one of the most extensively documented examples. Amnesty International's Security Lab published a major technical analysis in July 2026 describing the evolution of Pegasus and examining internal material disclosed through litigation involving NSO Group. The investigation described sophisticated infection methods, including zero-click techniques, in which an attacker could attempt to compromise a device without requiring the target to click a malicious link. Amnesty's analysis also found evidence that Pegasus systems involved customer-specific attack infrastructure and that NSO Group continued to maintain and develop the technology used by its customers.
The significance of Pegasus is not that it proves every allegation made about phone hacking. Its importance lies in demonstrating what modern commercial spyware can actually do. According to the Pegasus Project investigation, forensic examinations of phones identified infections and attempted infections involving journalists and activists in multiple countries. OCCRP reported that Pegasus can allow operators to access information on a device and potentially activate functions such as microphones and cameras. Researchers emphasized that forensic analysis, rather than merely the appearance of a phone number on a targeting list, provides the strongest evidence that a device was actually compromised.
The distinction between targeting and infection is particularly important. A telephone number appearing in a surveillance database does not necessarily mean that the phone was successfully hacked. A sophisticated surveillance system may attempt to infect a device and fail. Researchers therefore rely on technical traces found on the device itself to determine whether an infection occurred. This is one reason digital forensic analysis has become central to investigations involving commercial spyware.
There is also an important distinction between surveillance and evidence fabrication. A spyware operator gaining access to a smartphone does not automatically mean that the operator can rewrite every part of the user's digital history or manufacture an entirely convincing alternative history. Different devices, operating systems and applications have different security architectures and vulnerabilities. Some attacks may provide extensive access, while others may be more limited. Security updates can close vulnerabilities, and attack techniques can stop working when software changes. Amnesty's 2026 analysis specifically noted that Pegasus infection vectors can be disrupted by software updates and require continued technical development and maintenance.
That does not eliminate the possibility of manipulation. It means that the question has to be investigated technically rather than assumed.
Digital evidence has always required authentication, but smartphones have made that process both more valuable and more complicated. Consider a photograph found on a phone. Investigators may want to know when it was created, where it originated, whether it was downloaded from another source, whether it was subsequently modified and whether the copy recovered from the device matches other copies stored elsewhere. A text message can raise similar questions. Investigators may examine the device database, application records, server-side information, backups and records from the recipient's device. A document may be checked for creation and modification information as well as corroborating records outside the device.
This means that the security status of a phone can become part of the evidence itself. If forensic investigators establish that a device was compromised before a disputed file appeared, that fact may require additional scrutiny. It does not automatically prove that the file was planted, but it can change the questions investigators need to ask about authenticity and chain of custody.
There are precedents showing why these concerns are not merely theoretical. Researchers have previously documented hacking operations in which attackers allegedly placed incriminating documents on compromised computers. One widely discussed case involved the ModifiedElephant campaign in India, which researchers associated with the alleged targeting of activists and the placement of documents on their devices. The broader lesson from such investigations is that compromised computers can potentially become part of an effort to manipulate not only private information but also the evidentiary environment surrounding a target.
That does not establish that the same technique was used in Netanyahu's example, and it would be inaccurate to suggest that every spyware infection involves evidence planting. It does demonstrate, however, why cybersecurity specialists and forensic investigators take device compromise seriously when assessing disputed digital material.
The issue is particularly sensitive when the person holding the phone is a journalist. Reporters frequently communicate with confidential sources, lawyers, editors and other people whose identities may need protection. A compromised phone could expose source information, unpublished documents, interview records and future reporting plans. For journalists covering national security or armed conflict, the risks can be even greater because their devices may contain information involving military officials, government sources or people living in dangerous environments.
This is one reason the Pegasus controversy has attracted international attention. The technology was marketed as a tool for governments seeking to investigate serious crime and terrorism, but investigations have also documented its use against people whose work involved journalism, political opposition, human rights and public accountability. A 2026 investigation by Amnesty International provided further technical evidence about how Pegasus systems operate and how researchers can identify activity associated with specific deployments.
In July 2026, another case demonstrated that the controversy surrounding commercial spyware remains active. Citizen Lab reported that former European Parliament member Stelios Kouloglou's iPhone had been infected with Pegasus multiple times while he was involved with parliamentary investigations into surveillance. The researchers did not attribute the attacks to a particular government. That limitation is significant because technical evidence of infection does not automatically identify who ordered or conducted the operation. Nevertheless, the case illustrated the continuing ability of commercial spyware to compromise the devices of individuals involved in investigating surveillance itself.
The incident also illustrates a crucial principle in cybersecurity investigations: technical attribution and political attribution are not the same thing. Researchers may be able to establish that Pegasus was used against a particular device without being able to establish which government or organization was responsible. Attribution can require evidence from infrastructure, targeting patterns, technical fingerprints, intelligence information and other sources. Making the jump from “this device was infected with Israeli-developed spyware” to “the Israeli government hacked this person” requires additional evidence.
The same caution applies to Netanyahu's statement. He was explaining how a smartphone could theoretically be used to construct a damaging narrative about its owner. His remarks demonstrate that he considers digital manipulation a serious component of modern information warfare. They do not independently establish that Israel has hacked the phones of journalists or that Israeli authorities can plant evidence whenever they choose.
The broader context of his comments was the information battle surrounding Israel. In the CBS interview, Netanyahu argued that social media had become a major front in the conflict and linked declining support for Israel in the United States to the growing influence of social media. He said Israel had made extensive efforts to communicate with civilians during military operations and argued that social platforms had become central to how people perceive the conflict.
That brings the discussion to another technological development: artificial intelligence.
Even without compromising someone's smartphone, an attacker today can potentially create convincing synthetic material using AI. Text can be generated to imitate a person's style. Images can be manipulated. Audio can be synthesized. Video can be altered. Fake screenshots can be created. A fabricated conversation can be presented as though it came from a messaging application. The existence of these technologies makes authentication increasingly important.
The combination of hacking and AI could create an especially difficult environment. A compromised device could provide genuine personal information that is then combined with fabricated material. Real photographs could be mixed with altered ones. Genuine messages could be placed alongside fake messages. Authentic conversations could be selectively edited and presented without context. The resulting narrative could appear convincing precisely because some of its components are real.
This is where the concept of digital trust becomes critical.
For years, digital evidence was often regarded as particularly persuasive because computers seemed to provide precise records. A timestamp appeared objective. A photograph appeared concrete. A location record appeared measurable. A message seemed to preserve exactly what someone had written.
Modern cybersecurity has complicated that assumption.
The question is no longer simply whether information exists on a device. Investigators increasingly need to establish how that information got there, who had access to the device, whether the device was compromised, whether the information exists independently elsewhere and whether other evidence corroborates it.
This does not mean that digital evidence is inherently unreliable. On the contrary, digital forensics can produce extraordinarily detailed and reliable evidence when properly conducted. The important point is that reliability depends on methodology.
The chain of custody matters.
Original files matter.
Independent backups matter.
Server records matter.
Device logs matter.
Forensic imaging matters.
Corroboration matters.
And the possibility of compromise must be considered when there is technical evidence that a device was targeted.
The debate also exposes a wider problem with the phrase “Israel can hack any phone.” Cybersecurity capabilities are not universal keys. Even extremely sophisticated spyware depends on particular vulnerabilities, technical conditions and attack infrastructure. Devices run different operating systems and software versions. Security updates can eliminate known vulnerabilities. Some attack attempts fail. Some devices may not be susceptible to a particular exploit.
Amnesty International's latest technical analysis of Pegasus underscores this reality. The researchers described multiple infection vectors and explained how software updates can break those vectors, requiring new technical capabilities. The report also noted licensing restrictions and customer-specific infrastructure associated with Pegasus deployments.
Therefore, saying that sophisticated spyware exists is supported by evidence. Saying that a particular actor can penetrate any phone under any circumstances is a much broader proposition for which the available evidence does not provide a sufficient basis.
There is another distinction that deserves attention: the difference between Israeli technology companies and the Israeli state.
NSO Group is an Israeli company that developed Pegasus. Its technology has been sold to government customers under licensing arrangements. Reports and investigations have documented Pegasus use in numerous countries. But the fact that technology was developed in Israel does not automatically establish that the Israeli government was responsible for every operation involving it.
This distinction becomes particularly important when discussing international cases. In the 2026 case involving the former European Parliament member, Citizen Lab identified Pegasus infection but did not attribute the attack to a particular government.
The same principle applies to other cases involving commercial spyware.
Technology can provide the capability.
Forensic evidence can establish that the capability was used.
Additional intelligence and investigative evidence may be needed to establish who directed the operation.
And separate evidence may be needed to establish what the operator actually did after gaining access.
These are different questions.
The history of Pegasus has also demonstrated why regulatory questions have become so difficult. Commercial spyware has effectively expanded access to capabilities that were once associated primarily with state intelligence agencies. Governments can acquire sophisticated surveillance tools from private companies, creating a market in which highly intrusive technology crosses national borders.
This has produced repeated debates about export controls, human rights safeguards, government oversight and accountability.
The controversy is not limited to Israel. Pegasus has been linked through investigations to surveillance operations involving multiple governments. The 2026 reporting on Morocco, for example, presented additional evidence concerning the country's alleged use of Pegasus, while Moroccan authorities have denied using the spyware.
This broader international context is important because it demonstrates that commercial spyware has become a global issue rather than a purely Israeli one.
The underlying technology also changes the meaning of personal security.
A person may follow conventional cybersecurity advice, use strong passwords and install software updates, yet still face risks from highly sophisticated targeted attacks. That does not make basic cybersecurity measures useless. Updates remain essential because they close vulnerabilities that attackers may otherwise exploit. But highly targeted surveillance can operate at a level beyond the ordinary threats most people encounter.
For governments, journalists and other high-risk individuals, the response may involve additional precautions such as dedicated devices, security reviews, minimizing sensitive information stored on phones and using specialized forensic examinations when compromise is suspected.
The most important lesson, however, may be about evidence.
If a phone has been compromised, investigators should not automatically assume that every file on it is false. That would be just as problematic as assuming that everything on an apparently normal phone is unquestionably authentic. Instead, each disputed piece of evidence should be evaluated according to its provenance, technical characteristics and independent corroboration.
A photograph should be compared with its original source when possible.
A message should be examined alongside records from the other participants.
A document should be checked against server and cloud records.
Location information should be compared with independent telecommunications or physical evidence where available.
And forensic investigators should determine whether the device shows signs of compromise.
This approach does not guarantee certainty, but it makes manipulation considerably more difficult.
Netanyahu's warning ultimately points toward a larger transformation in the information environment. In earlier eras, propaganda primarily depended on controlling newspapers, radio and television. The internet dramatically expanded the number of people who could publish information. Social media accelerated distribution. Smartphones created an enormous stream of personal information. AI is now making the production of convincing synthetic content increasingly accessible.
The result is an environment in which the most dangerous misinformation may not be entirely fake.
It may contain enough genuine material to appear authentic.
A real photograph can be paired with a false caption.
A genuine conversation can be presented without its surrounding context.
A real recording can be edited selectively.
A genuine document can be mixed with a fabricated one.
A real phone can be compromised and its contents interpreted selectively.
The challenge is therefore not simply detecting fake information. It is determining the provenance and integrity of information.
That is why the phrase “plant the evidence” should be treated with particular care. Evidence can be fabricated in the digital age, but proving that evidence was fabricated requires more than demonstrating that a phone could theoretically be hacked. Investigators need technical evidence connecting the compromise to the disputed material.
This distinction becomes especially important when allegations involve governments, intelligence agencies or military operations. Extraordinary claims require evidence that can withstand independent scrutiny.
Netanyahu's statement has therefore opened a window into a much larger problem. The issue is not simply whether Israel has advanced cyber capabilities. It clearly has a sophisticated cybersecurity and cybertechnology ecosystem, and Israeli-developed spyware has demonstrated powerful surveillance capabilities. The issue is how societies should determine what is authentic when phones can be remotely compromised, information can be manipulated and AI can create convincing synthetic material.
The answer cannot be to distrust every digital record.
Nor can it be to trust every digital record.
The answer is to strengthen the systems that establish authenticity.
Independent forensic examination, secure evidence preservation, transparent investigative procedures and corroboration from multiple sources become increasingly important as technology advances.
The smartphone in a journalist's hand may look like an ordinary object, but it can contain an extraordinary amount of information about that person's life. It can also become a target in the wider struggle over information, privacy and political narratives.
That is the deeper meaning behind Netanyahu's words, “You're not immune either.”
The statement was made during an argument about social media and Israel's international image, but the technological reality extends far beyond that particular dispute. No journalist, politician, business leader or ordinary citizen should assume that a smartphone is inherently invulnerable. At the same time, no government, company or individual should be accused of hacking a particular device or planting evidence without evidence capable of supporting that claim.
The digital age has created a new problem for journalism, law enforcement and courts alike.
The question is no longer simply, “What does the phone contain?”
It is increasingly, “How do we know who put it there, when it got there, whether it was altered and whether independent evidence confirms it?”
As spyware becomes more sophisticated and artificial intelligence makes synthetic content harder to distinguish from authentic material, those questions will become central to the credibility of digital evidence itself.
The future battle may not be over who controls the phone.
It may be over who controls the truth that emerges from it.
#BeyondHeadlines #Netanyahu #Israel #CyberSecurity #Spyware #Pegasus #NSOGroup #PhoneHacking #CyberWarfare #DigitalEvidence #DigitalForensics #Surveillance #CyberEspionage #ArtificialIntelligence #AI #Deepfake #Disinformation #Misinformation #DigitalPrivacy #SmartphoneSecurity #InformationWarfare #CyberThreats #Journalism #TechnologyNews #IsraelNews #MiddleEast #DigitalSecurity #CyberTechnology #Privacy #HumanRights #BeyondTheHeadline